SOC2 Update
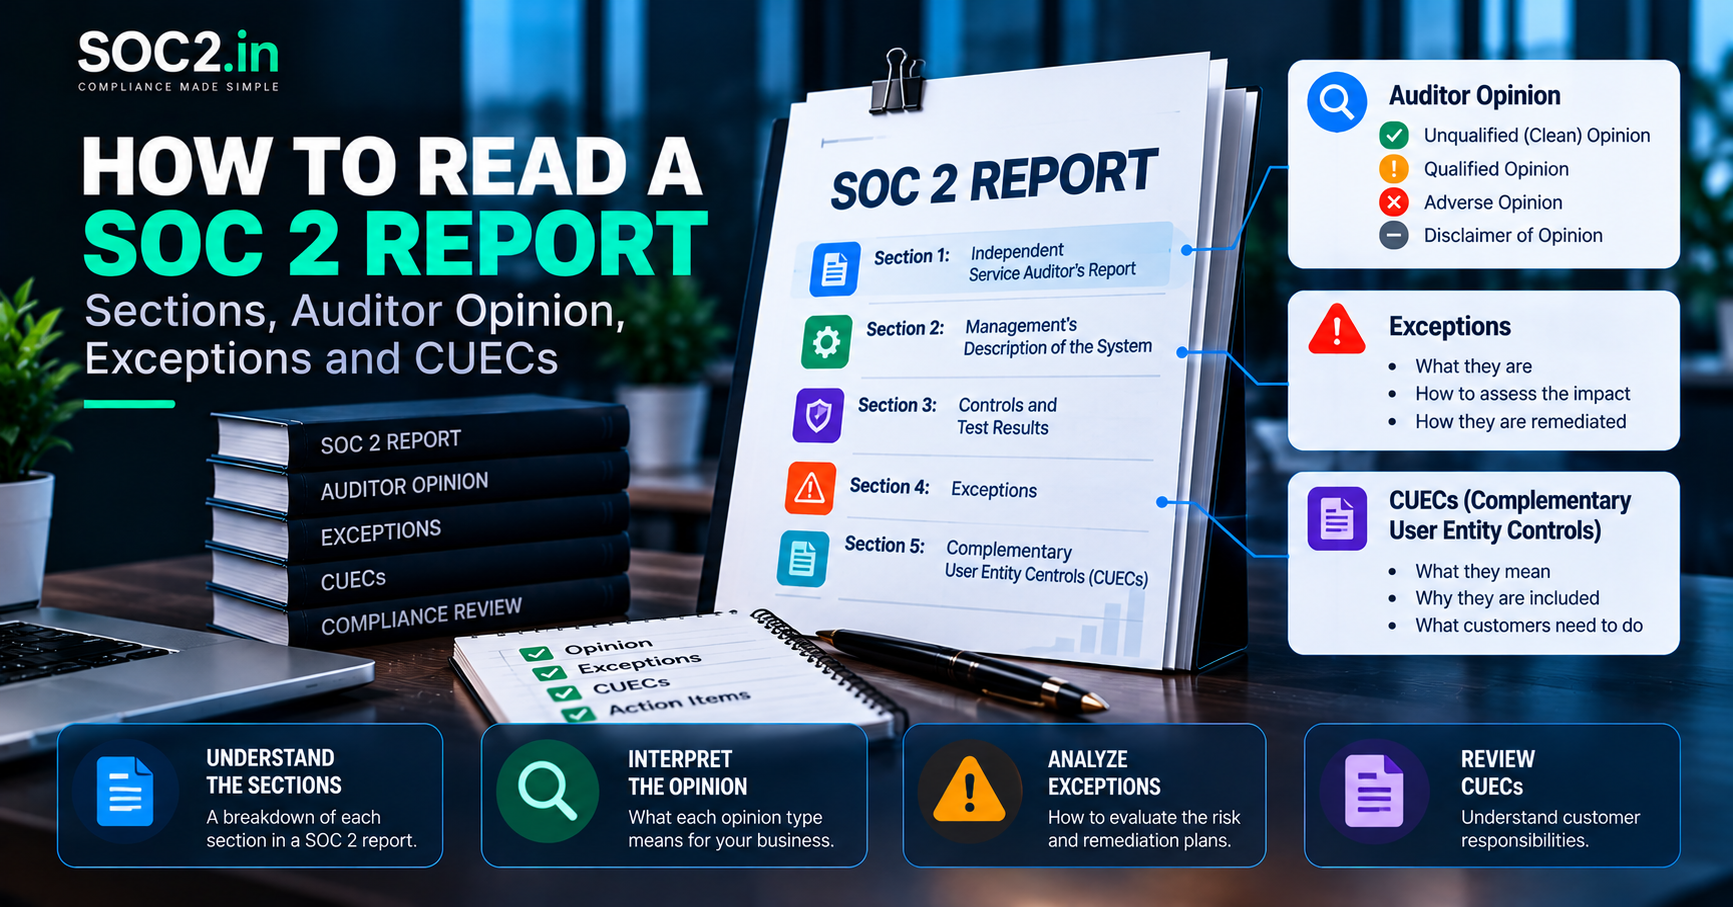
Learn how to read a SOC 2 report: the opinion, system description, test results, exceptions and CUECs, plus a vendor review checklist.
Learn how to read a SOC 2 report: the opinion, system description, test results, exceptions and CUECs, plus a vendor review checklist.
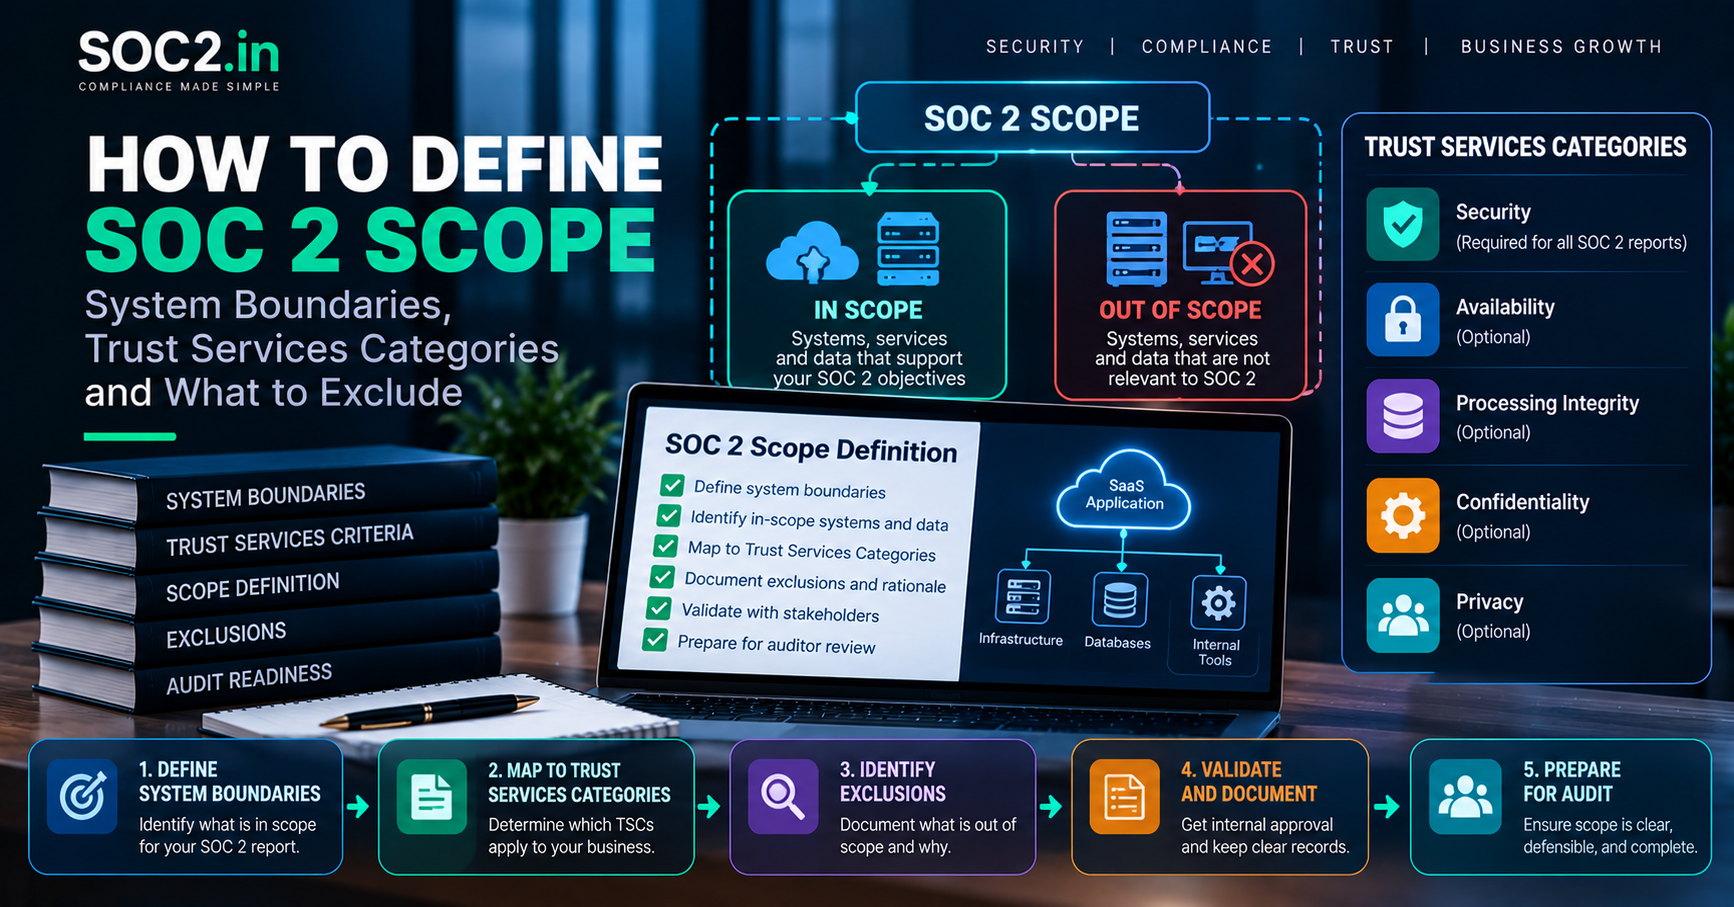
SOC 2 scope decides cost, timeline and what customers rely on. Learn how to set system boundaries, pick categories and handle exclusions.
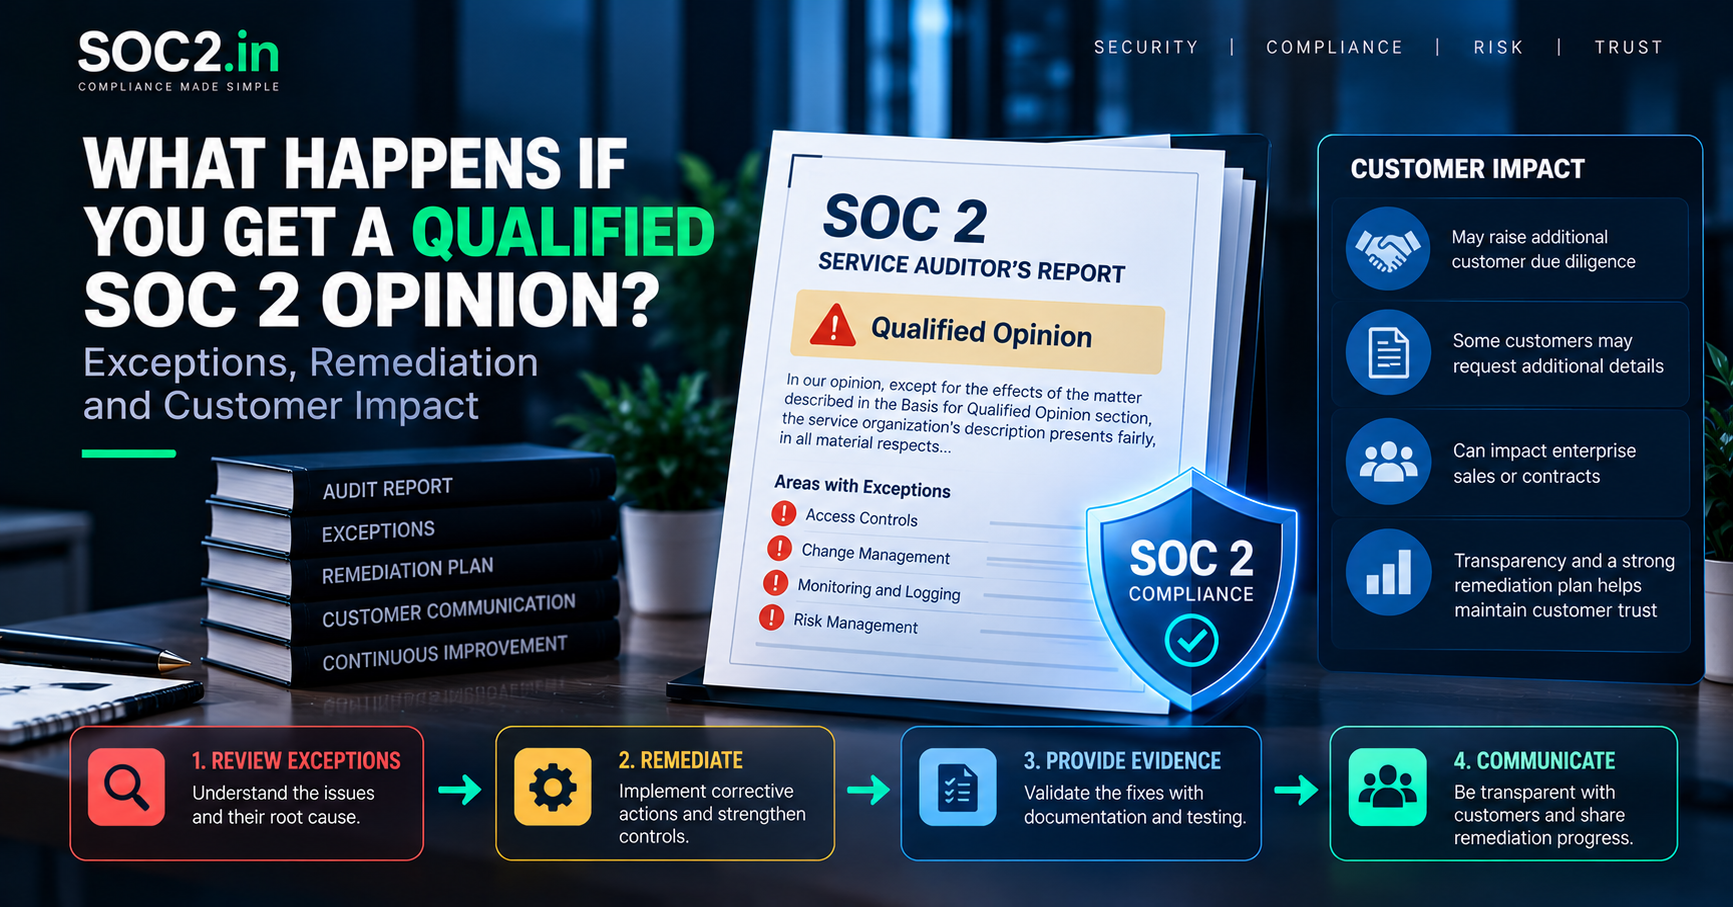
A qualified SOC 2 opinion is not a failed audit, but it matters. Learn what exceptions mean, how buyers react and how to recover.
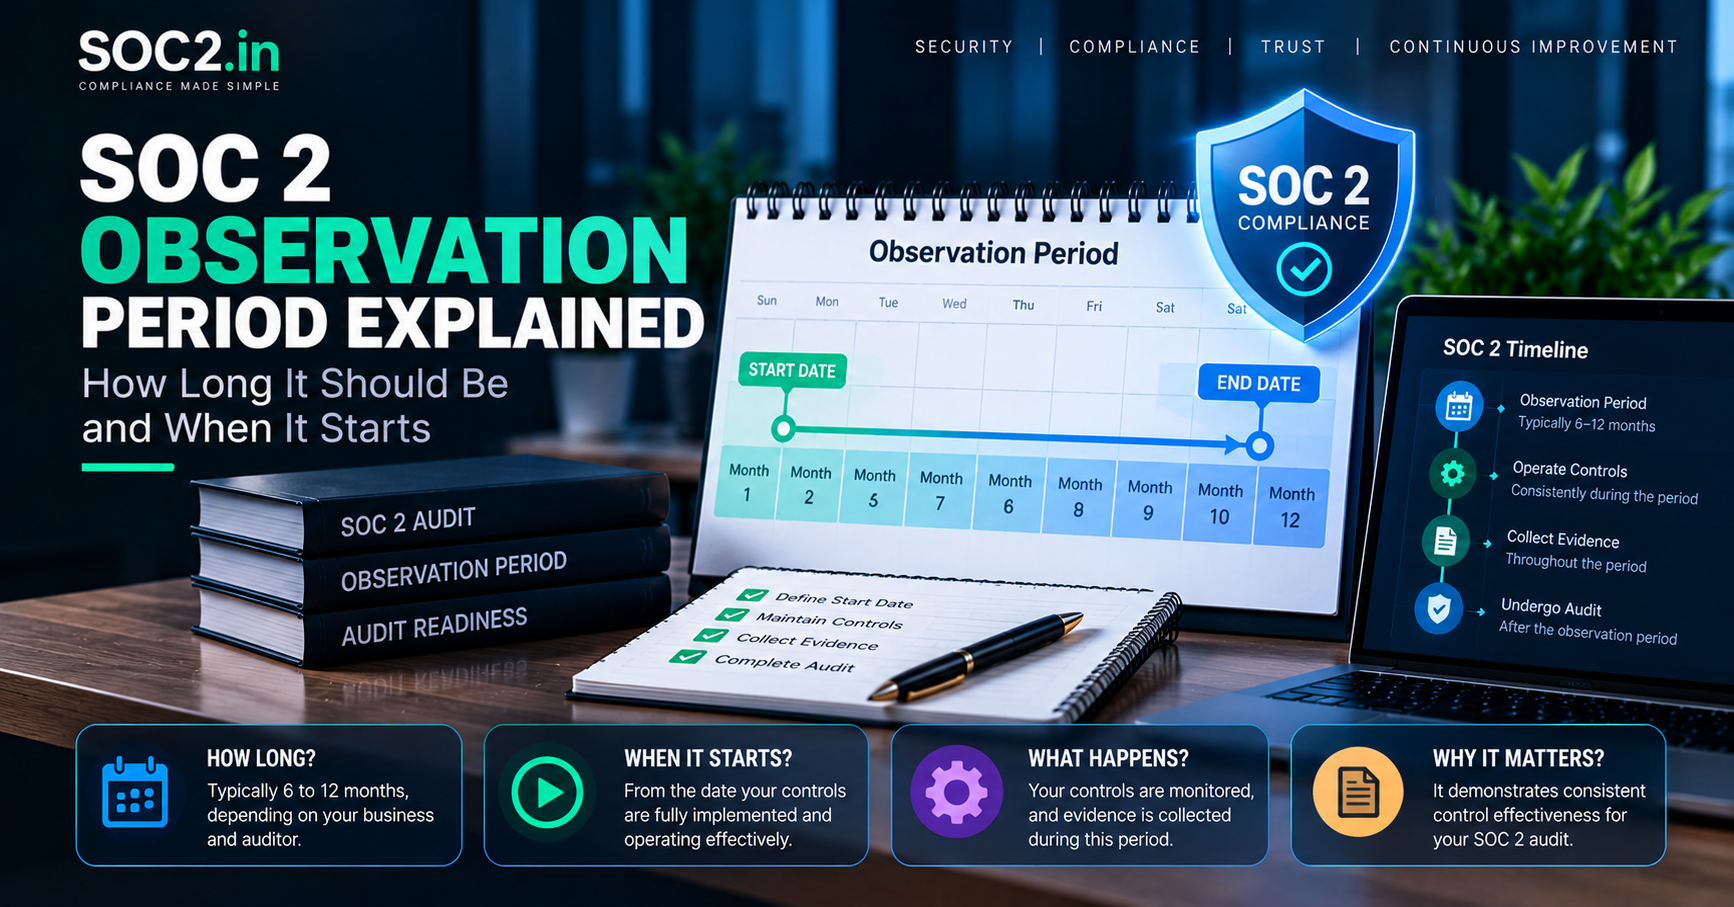
The SOC 2 Type II observation period is the window your controls must run and be tested. See how long it should be, when it
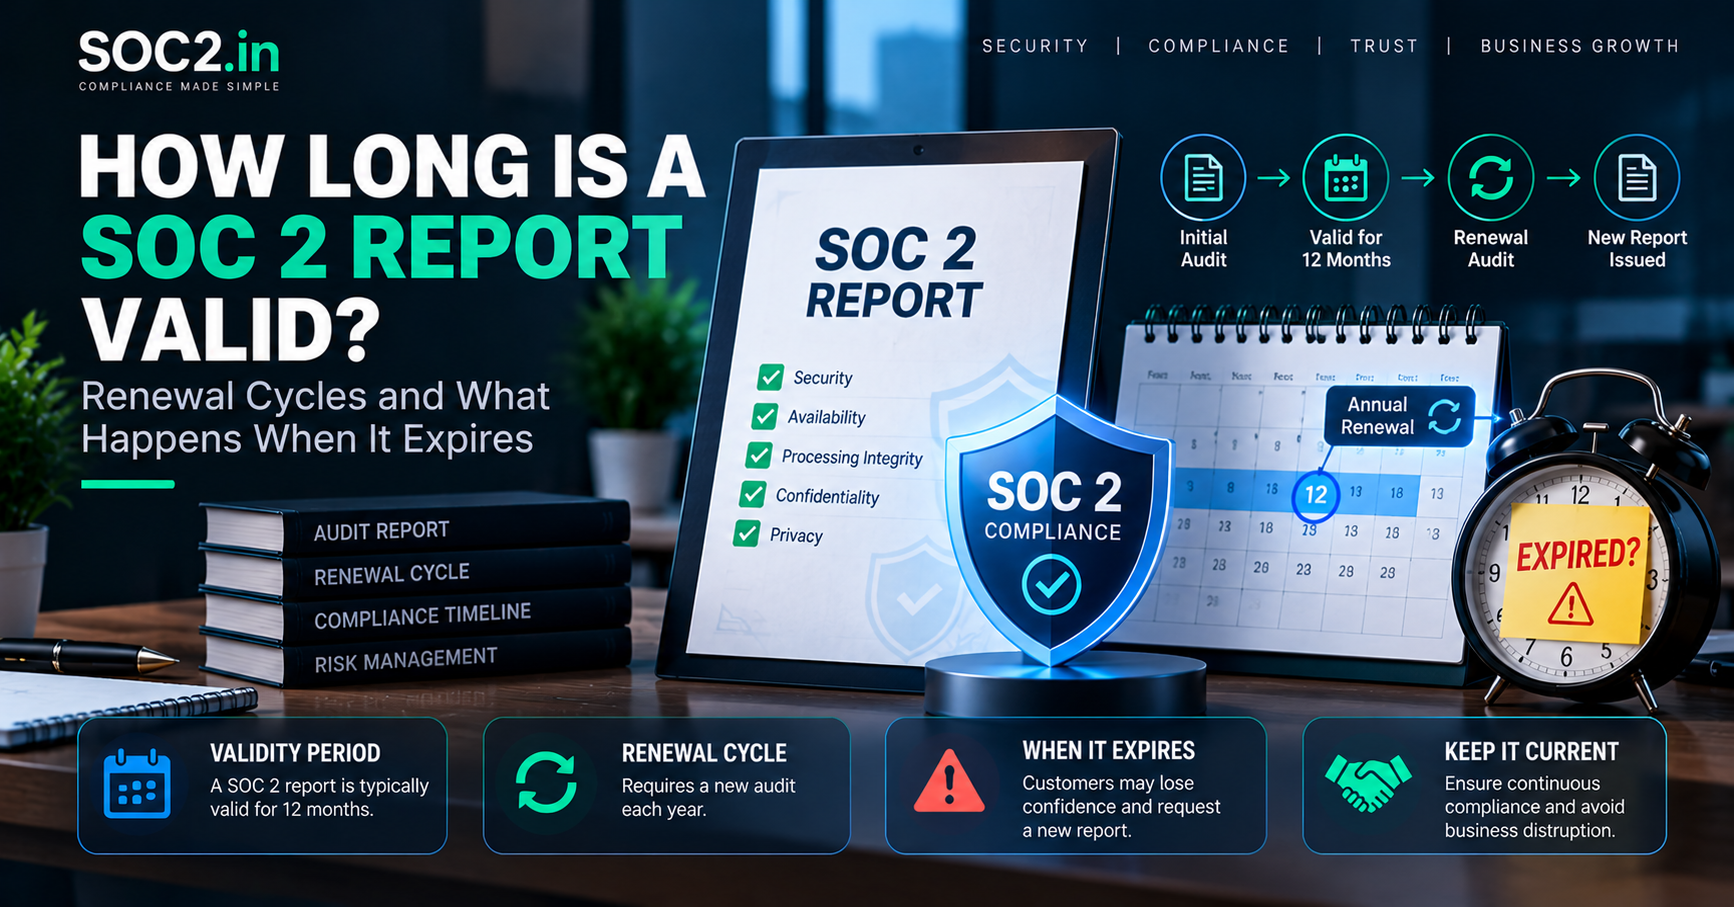
SOC 2 reports have no official expiry date, but most buyers want one from the last 12 months. Learn renewal timing and what to do
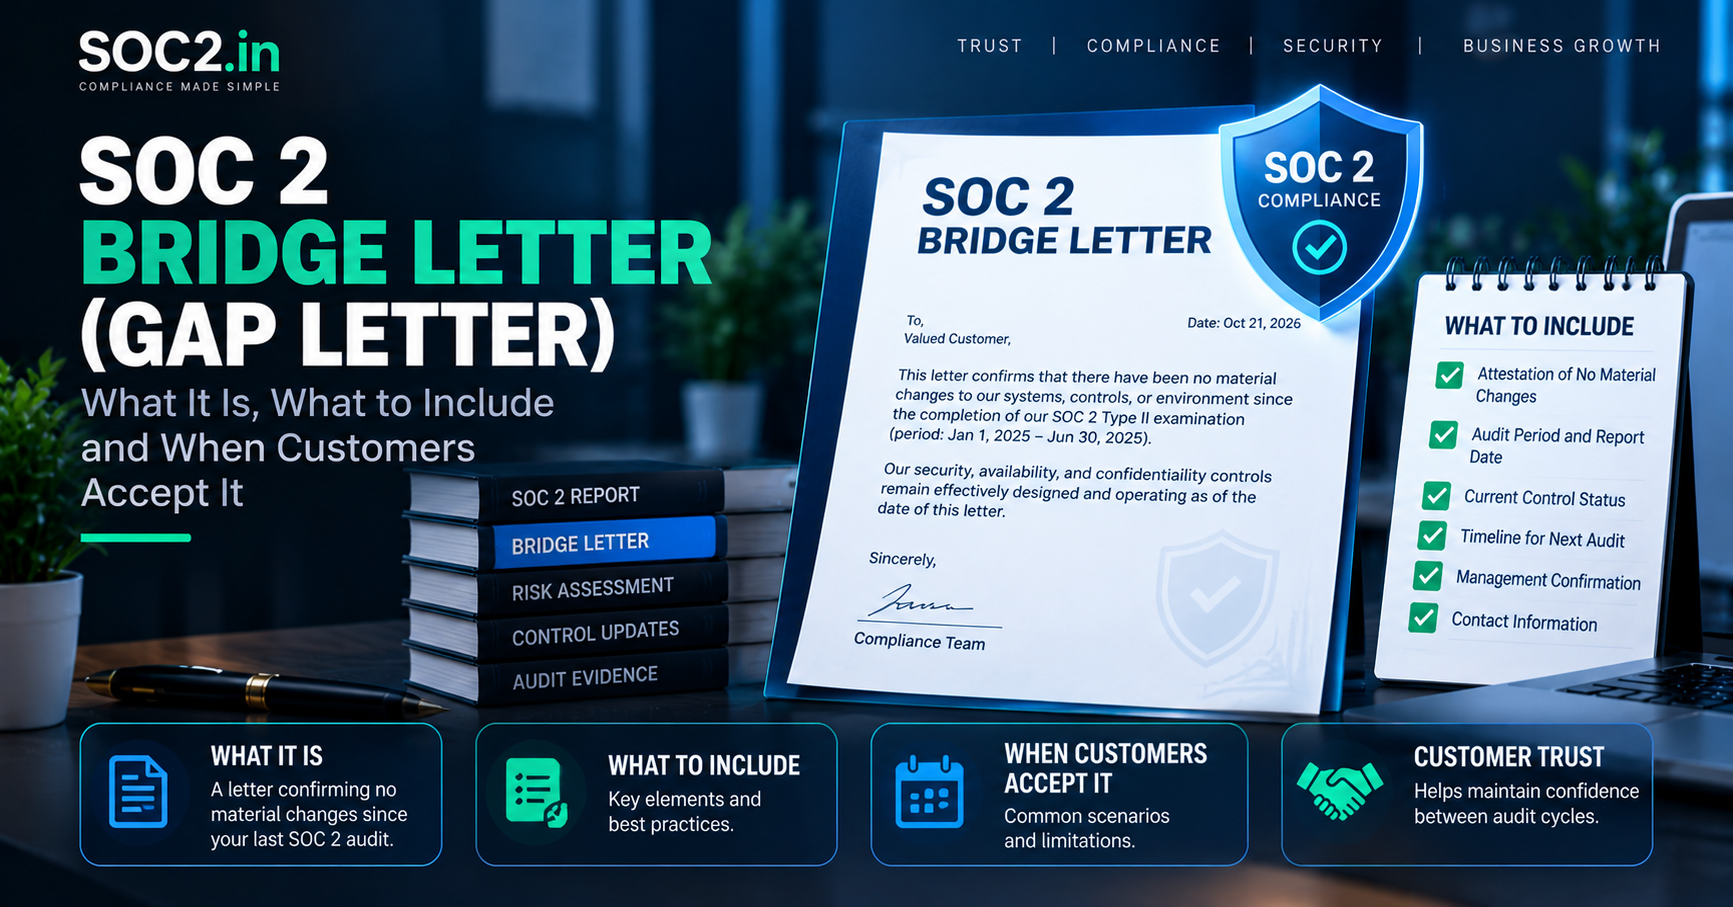
A SOC 2 bridge letter covers the gap between your last report and today. Learn what it contains, who signs it and when customers accept
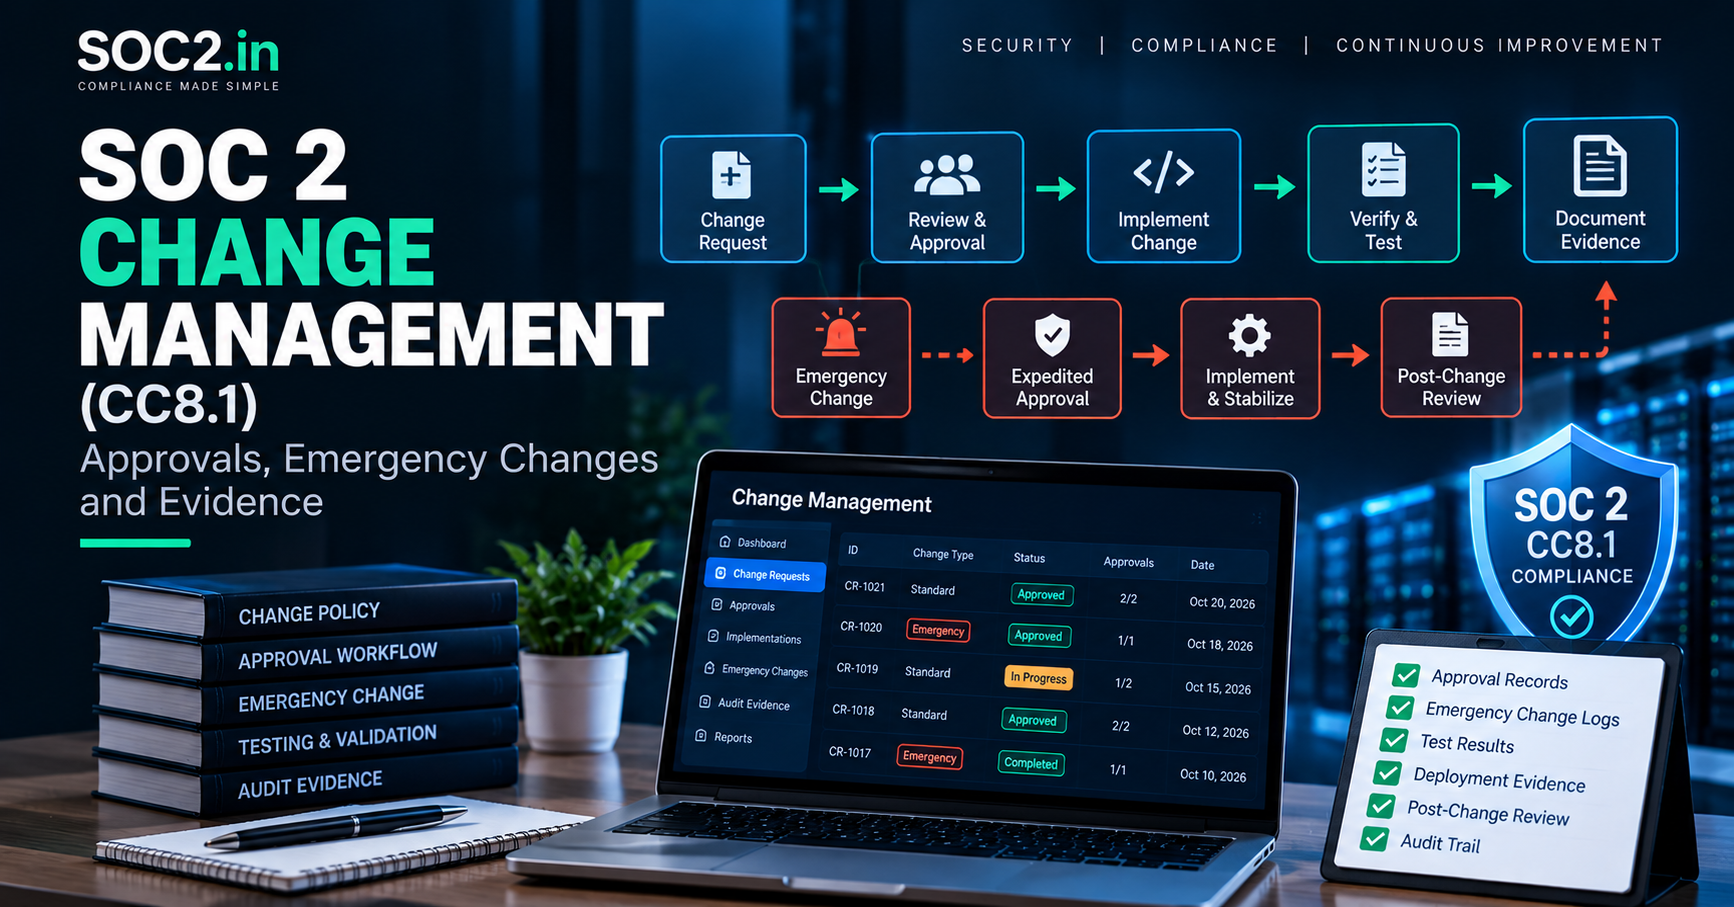
How SOC 2 change management works under CC8.1: required steps, segregation of duties, emergency changes, infrastructure changes and the evidence auditors sample.
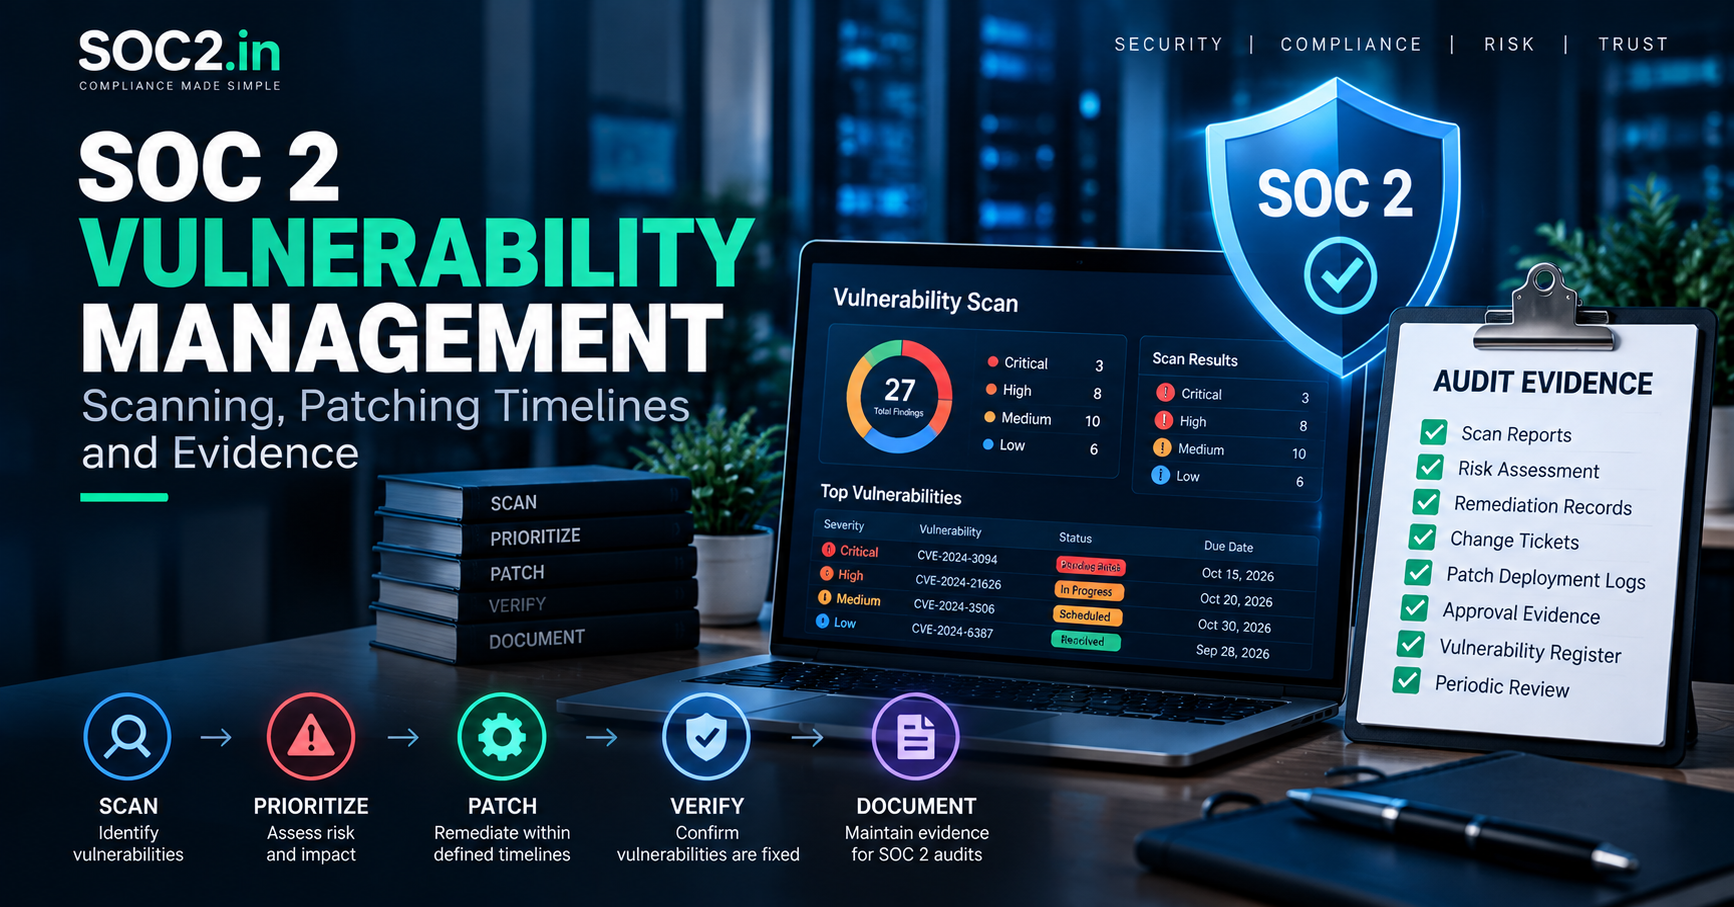
What SOC 2 expects for vulnerability management under CC7.1: scan types, remediation timelines, exceptions, and the evidence auditors request in a Type II period.
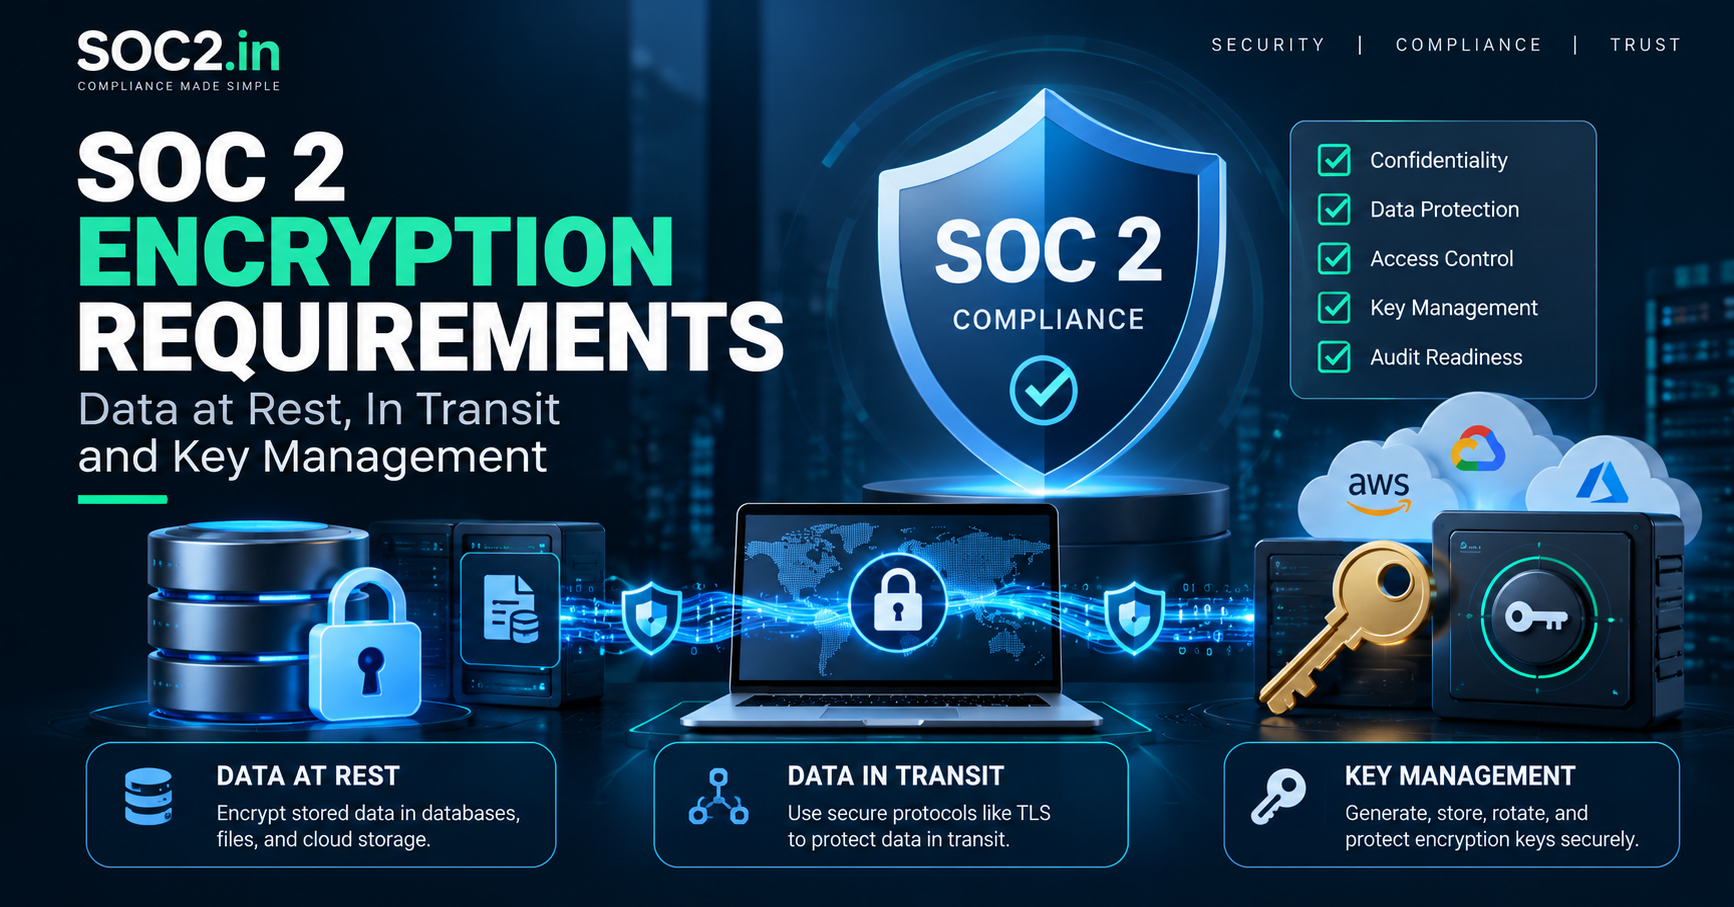
Does SOC 2 require encryption? What the Trust Services Criteria say about data at rest, data in transit and key management, and the evidence auditors

A SOC 2 audit typically takes 4 to 12 weeks, depending on the type of audit, the organization’s readiness, the number of controls being tested,