SOC2 Update
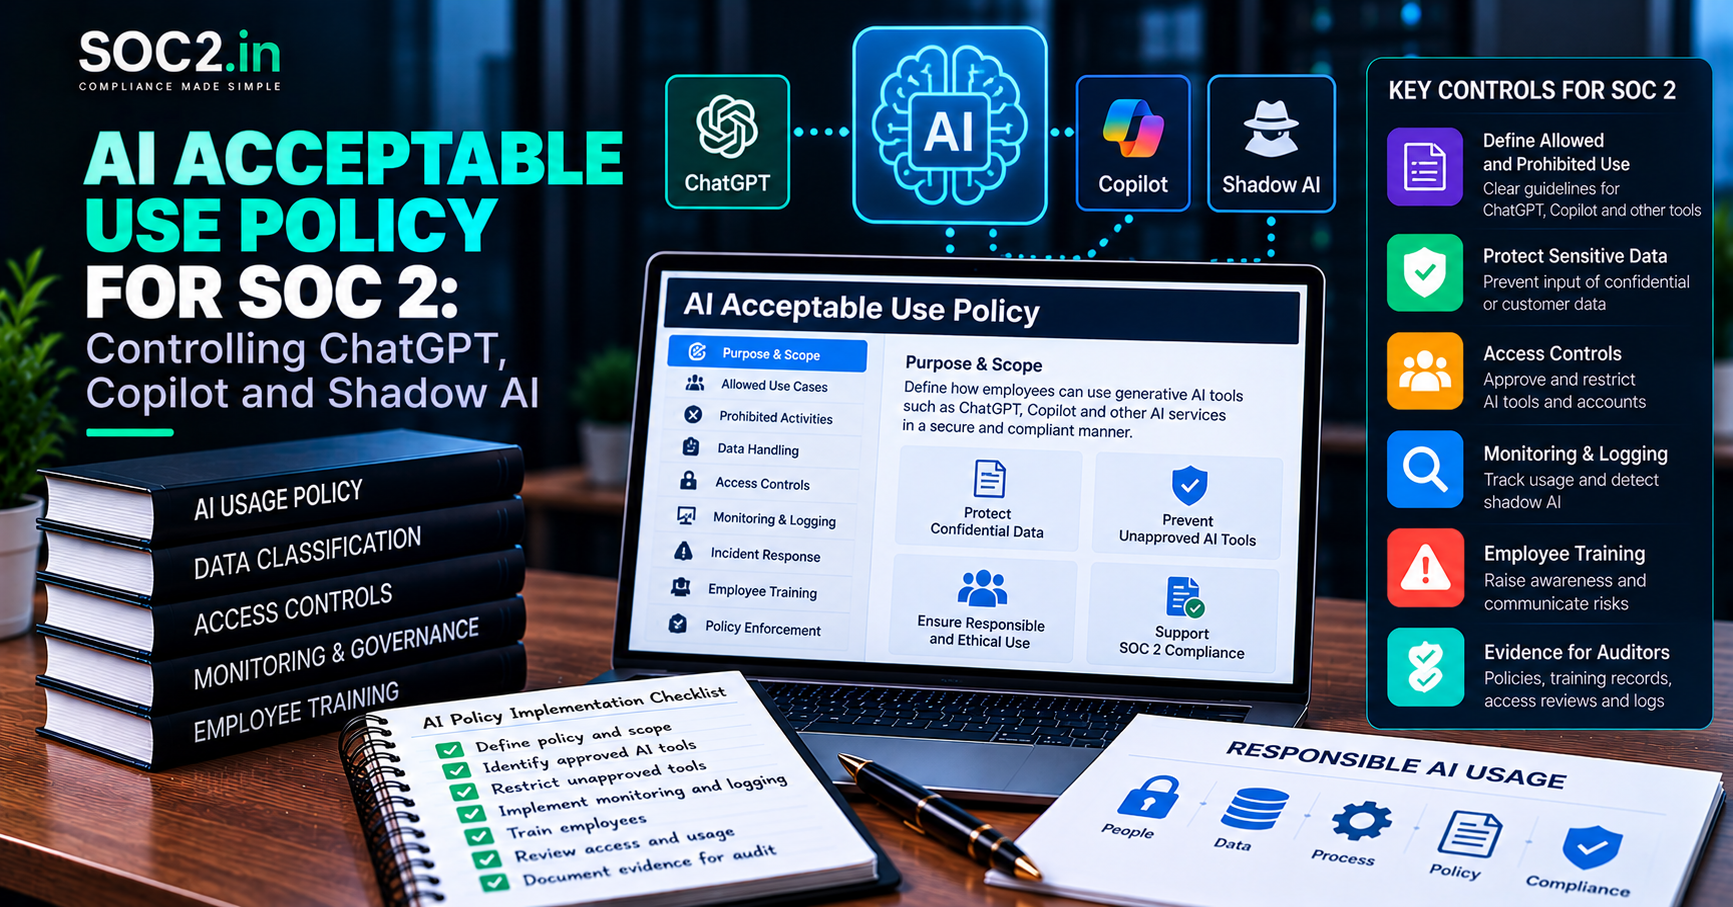
How an AI acceptable use policy supports SOC 2: how AI risks map to existing criteria, what the policy should contain and the evidence auditors
How an AI acceptable use policy supports SOC 2: how AI risks map to existing criteria, what the policy should contain and the evidence auditors
How to run a penetration test that supports SOC 2: scope, tester independence, timing in the observation period, remediation tracking and the evidence auditors request.
What SOC 2 expects for logging and monitoring: CC7.1 to CC7.4, a risk-based list of log sources, retention without invented rules, and the evidence auditors
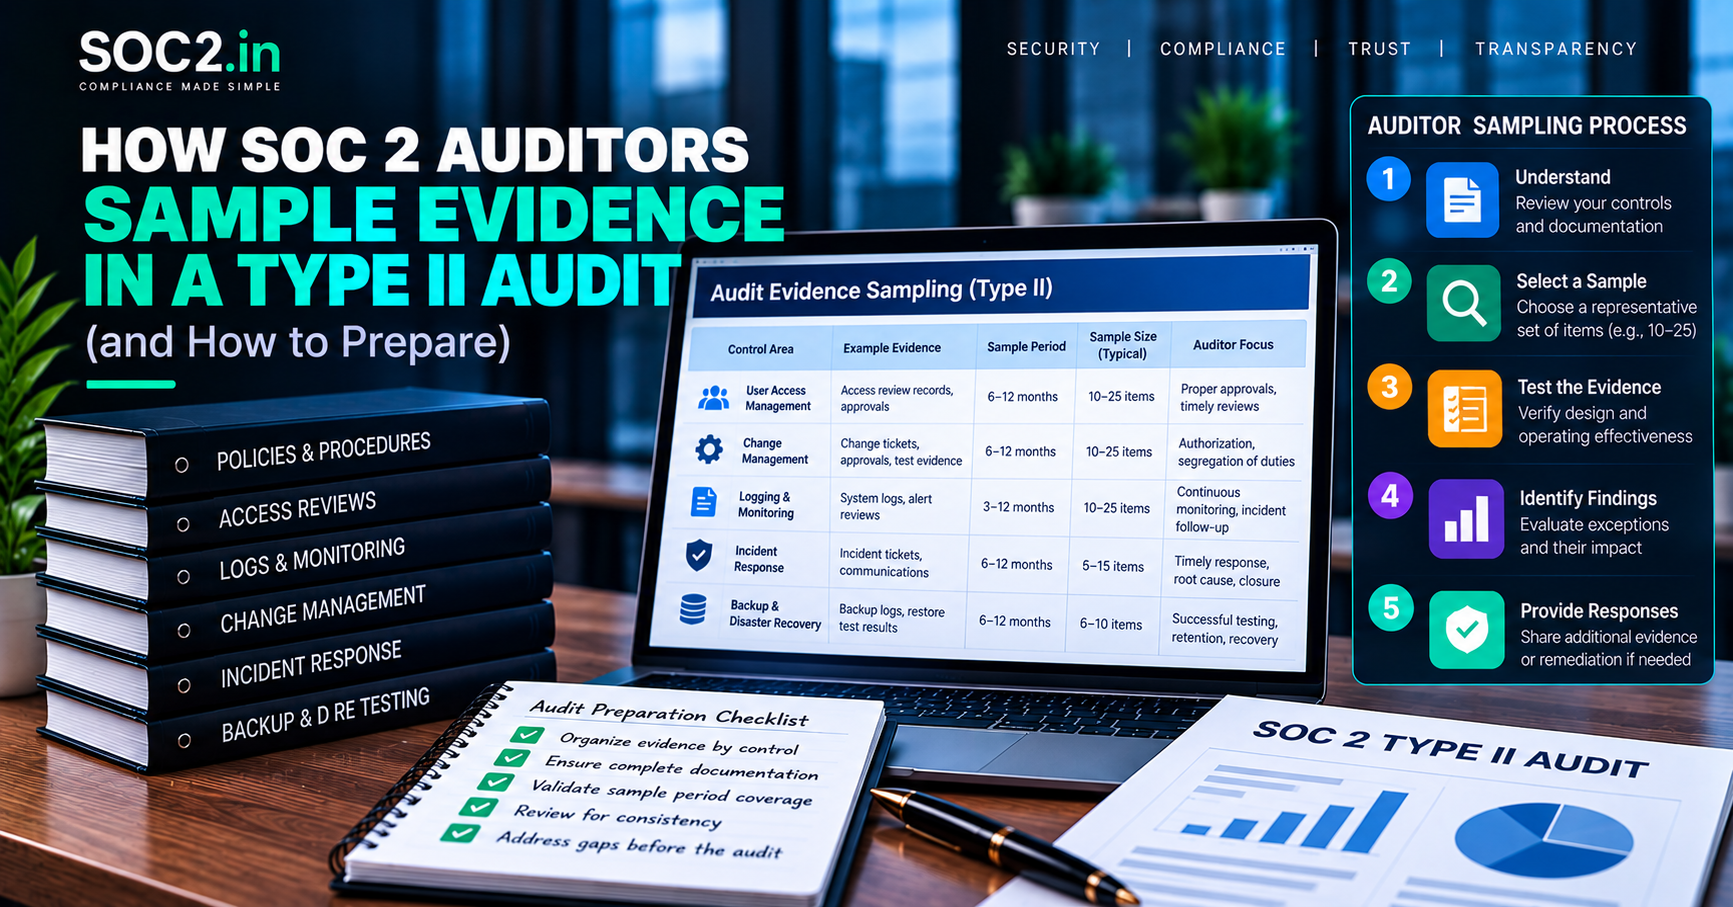
How SOC 2 Type II audit sampling works: populations, sample selection, completeness of data, exceptions and how to prepare your evidence.
How SOC 2 treats backups and disaster recovery: A1.2 and A1.3, RTO and RPO, restore tests, and the evidence auditors sample during a Type II
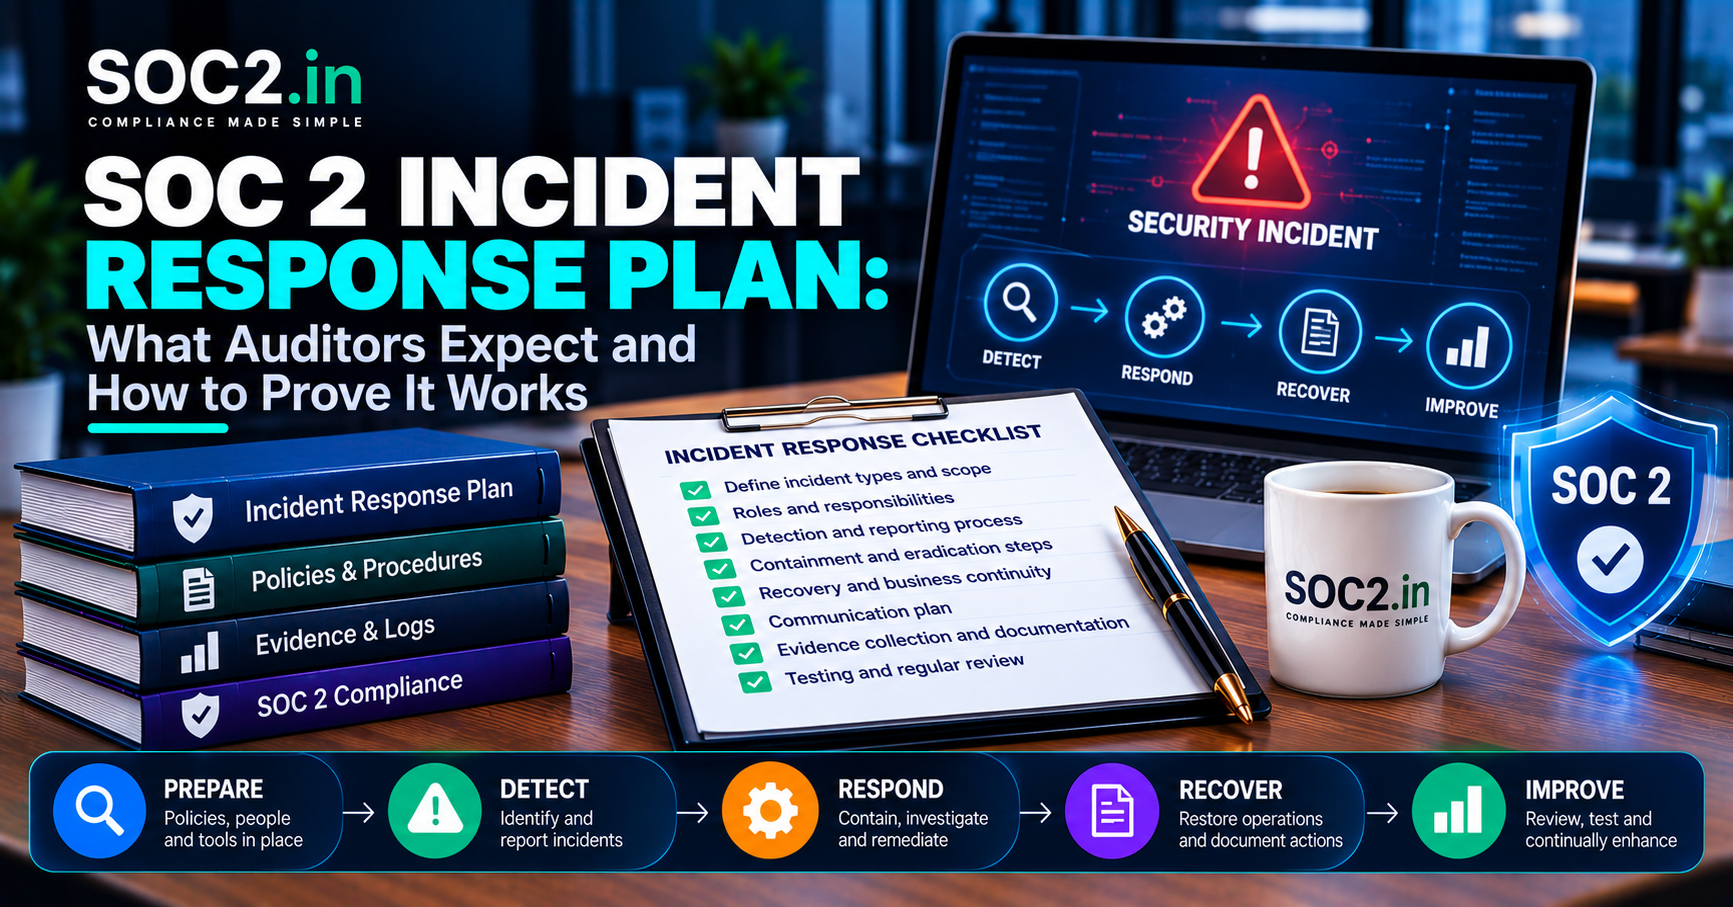
What a SOC 2 incident response plan must cover under CC7.3 to CC7.5, the evidence auditors sample in a Type II period, and how to
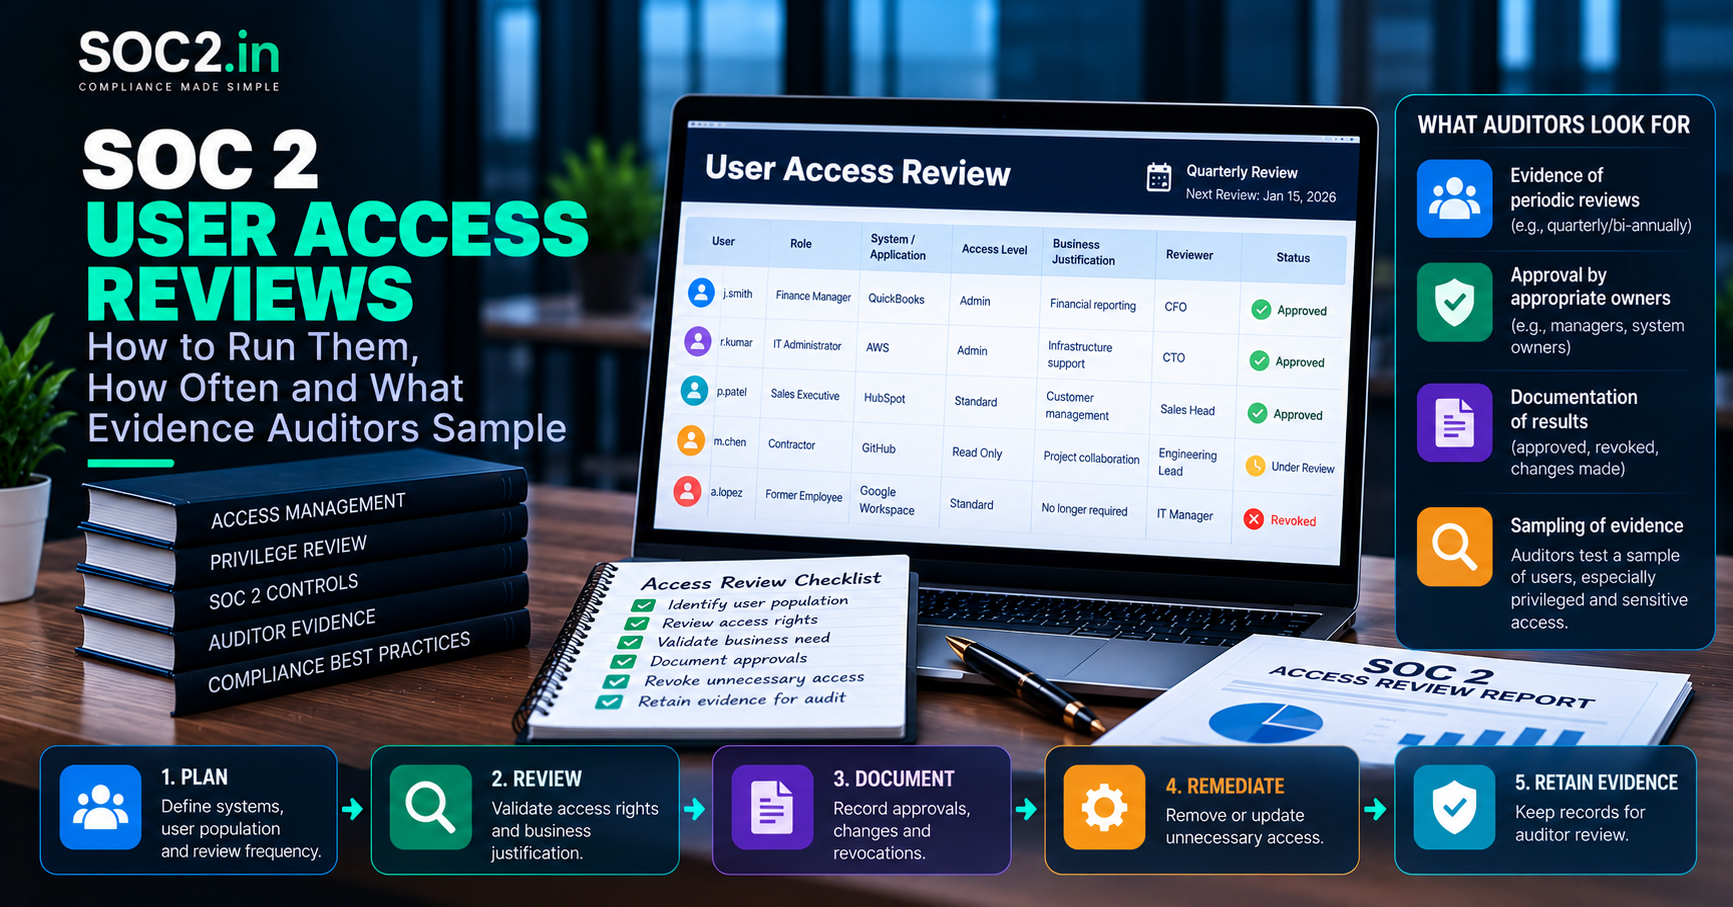
How to run SOC 2 user access reviews: how often, who reviews, what to check and the evidence auditors sample, with a step-by-step checklist.
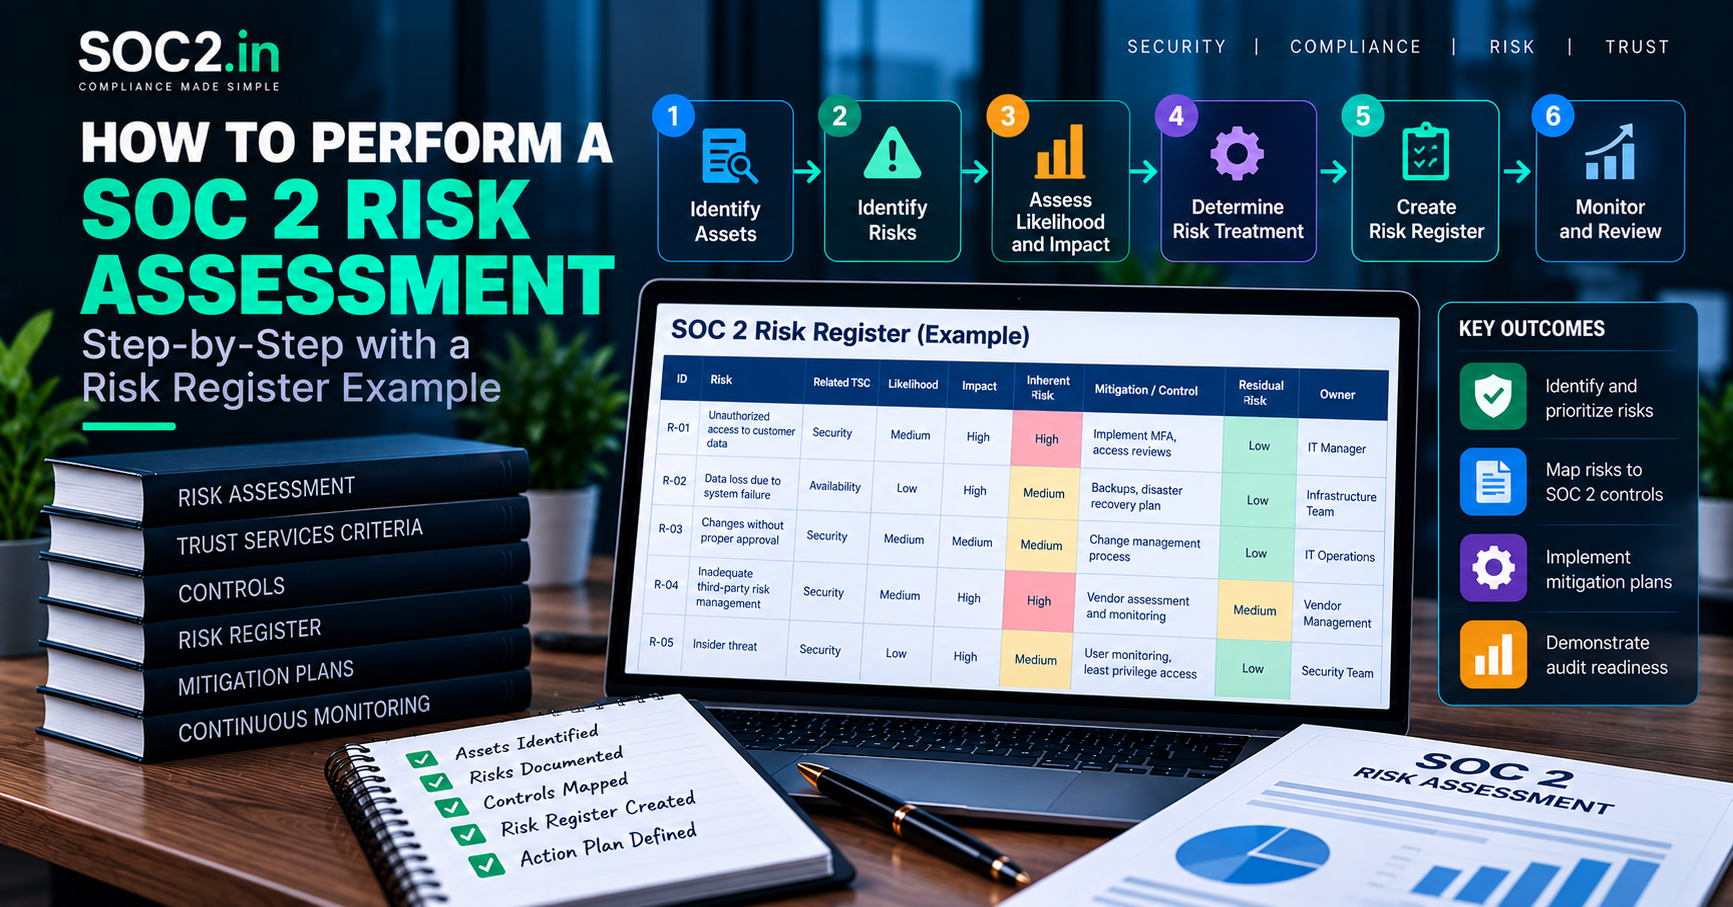
A SOC 2 risk assessment shows auditors you identify and manage risks. Follow these steps with a sample risk register and evidence list.
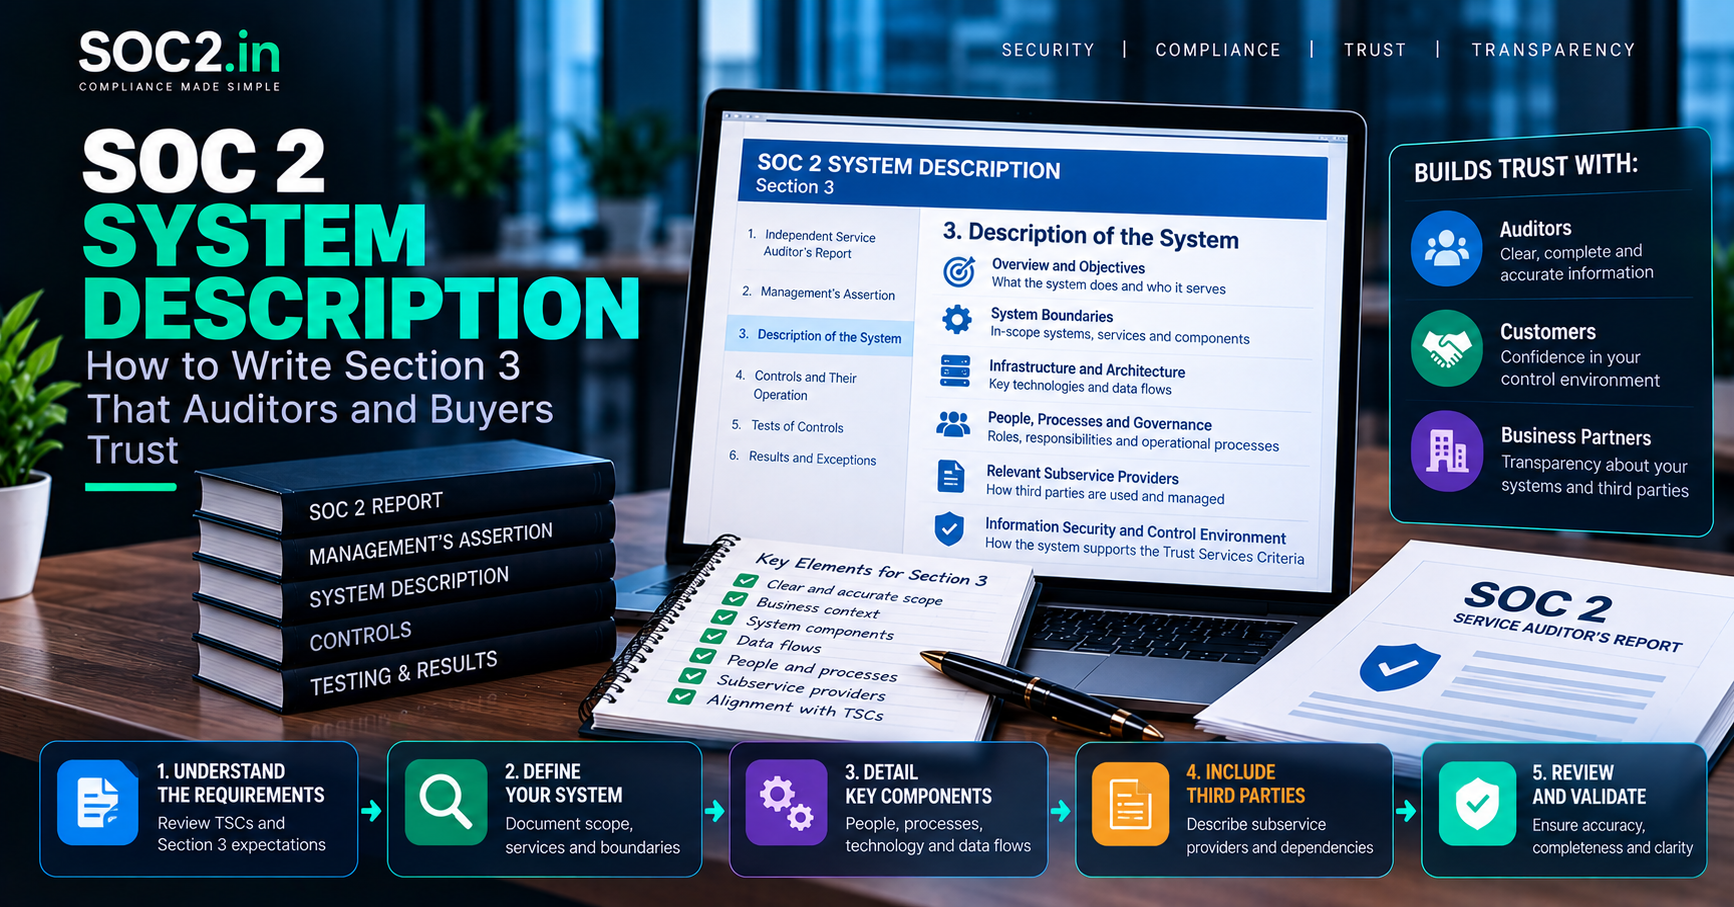
How to write a SOC 2 system description that auditors accept and buyers trust: required elements, structure, a sample outline and mistakes to avoid.
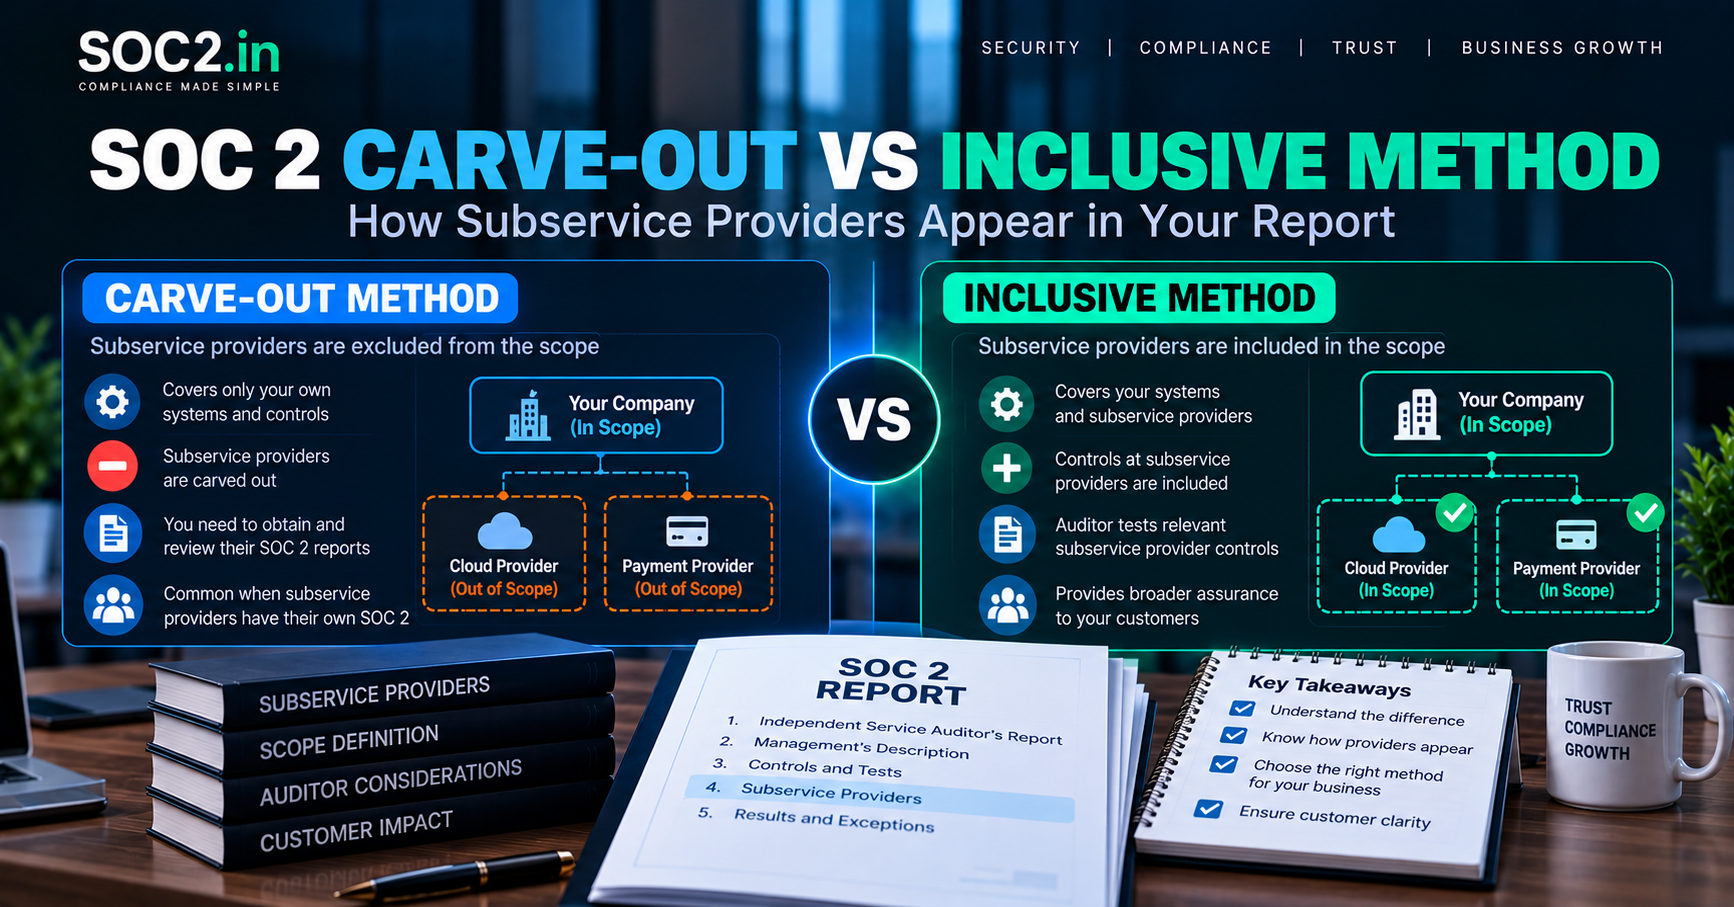
SOC 2 carve-out vs inclusive method: how subservice providers such as AWS appear in your report, what CSOCs are and what auditors expect.